Executive summary
A high-level view of the assessment and its risk implications.
02 / METHODOLOGY
Establish the environment, objectives, and testing boundaries. Make in-scope and out-of-scope activities explicit.
Follow realistic adversary behavior and investigate connected attack paths. Validate findings with supporting evidence.
Review risk-ranked findings, exploit paths, and control mappings alongside an executive summary.
Use practical recommendations to decide what needs attention and plan improvements.
DELIVERABLES
A high-level view of the assessment and its risk implications.
Attack paths, severity, impact, and supporting evidence for the issues identified.
Recommendations and links to control intent that support assessment review.
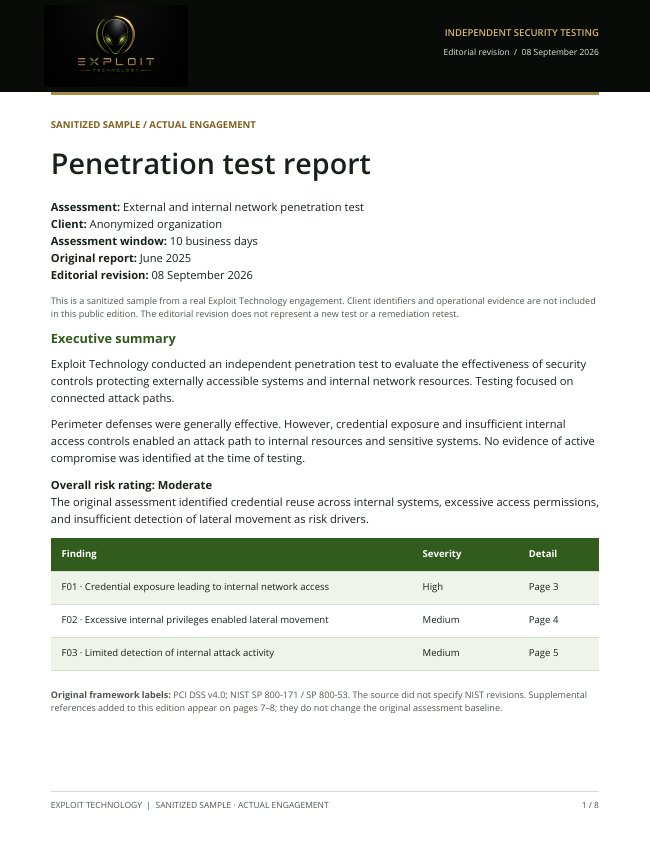
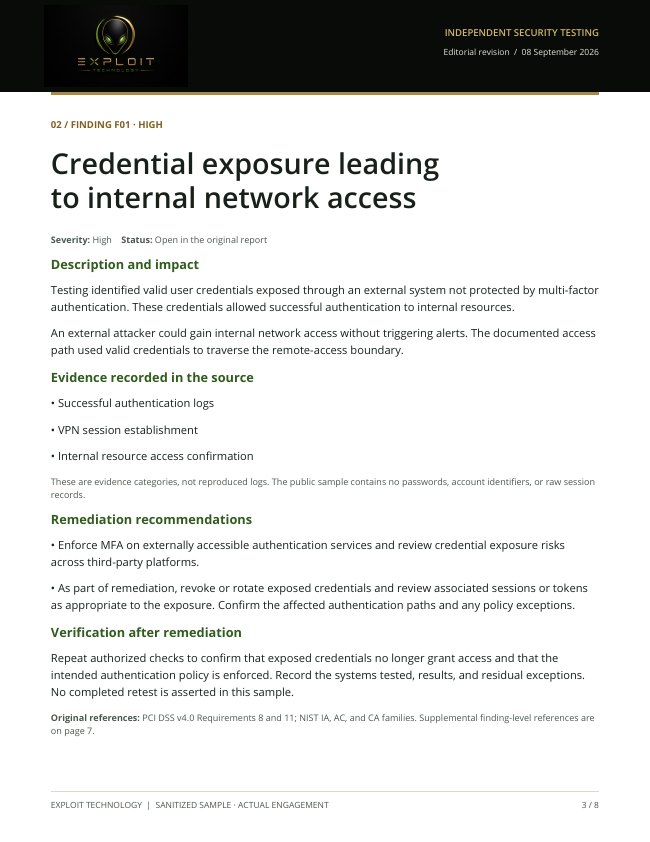
SAMPLE DELIVERABLE
Review a sanitized report from a real engagement, with scope, findings, remediation guidance, and supplemental PCI DSS v4.0.1 and NIST SP 800-53 Rev. 5 references.
Actual June 2025 engagement. Editorially revised in September 2026; supplemental references do not change the original assessment baseline.
Download sample PDF PDF · 8 pages · approximately 2 MBTESTING SCENARIO
Attack surface
Control boundaries
Connected exposure
Business impact
EXTERNAL SERVICES
Start with external services and the attack surface agreed in the scope. Identify plausible entry points and validate what is actually exposed.
How we approach testingLET’S TALK SECURITY
Discuss your environment, assessment needs, and next steps.