01
Penetration testing
Identify exploitable weaknesses through realistic attack scenarios tailored to your environment.
Understand how an attacker could get in.
INDEPENDENT SECURITY TESTING
Know where you’re exposed. Get clear findings and practical guidance to strengthen your security.
Discuss your assessment
01 / SERVICES
Focused assessments that connect technical findings to the decisions you need to make.
Identify exploitable weaknesses through realistic attack scenarios tailored to your environment.
Understand how an attacker could get in.
Independent technical testing to support assessors and validate the effectiveness of security controls.
Bring clear evidence to your assessment.
Assess detection, response, and containment capabilities against realistic attack scenarios.
Find the gaps before an incident.
02 / WHO WE HELP
Independent testing for organizations protecting sensitive information and assessing control effectiveness.
Technical evidence, segmentation validation, and risk-ranked findings to support independent assessments.
Independent support for QSAsSecurity assessments for environments where protecting patient information matters.
Validate controls and support evidence-based audits with practical testing.
Independent technical validation. Exploit Technology does not perform audits, certifications, or attestations, or guarantee audit outcomes.
03 / OUR APPROACH
A structured engagement, with direct contact with the practitioner performing your testing.
Agree the environment, objectives, access, and testing boundaries before work begins.
Investigate how exposed services, identity, and internal controls connect.
Explain the findings, business risk, and priorities in a practical report.
Use clear recommendations to plan improvements and strengthen defenses.
EXPOSURE / EXTERNAL SERVICES
Start with external services and the attack surface agreed in the scope. Identify plausible entry points and validate what is actually exposed.
ACCESS / IDENTITY & ACCESS
Examine authentication, permissions, and segmentation. Investigate whether one weakness creates access to another part of the environment.
IMPACT / CRITICAL SYSTEMS & DATA
Connect the attack path to systems and information that matter to the organization. Explain business risk with supporting technical evidence.
ACTION / CLEAR REMEDIATION
Translate the evidence into risk-ranked findings and practical remediation guidance so the team can decide what needs attention.
How we approach testingFROM TESTING TO EVIDENCE
Scope, findings, impact, and practical recommendations—brought together in a report your team can use.
Actual June 2025 engagement. Editorially revised in September 2026; supplemental references do not change the original assessment baseline.
Download sample PDF PDF · 8 pages · approximately 2 MB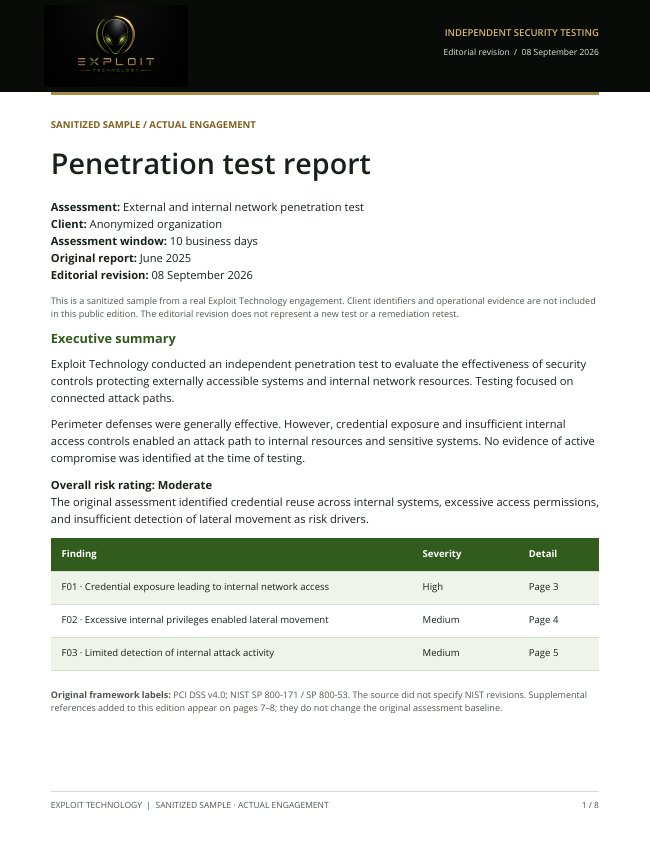
LET’S TALK SECURITY
Discuss your environment, assessment needs, and next steps.